Table of Contents
Start your free trial.
Table of Contents
Executive Summary
AI coding assistants promised to speed up software delivery, and they delivered. According to one report, developers are saving almost 60% of their time on coding tasks. Other velocity metrics look just as impressive.
As the engineering lead, you’re thrilled because the team delivered more features this quarter.
Then the security team flags three vulnerabilities, all of them in AI-generated code that passed the existing checks. Welcome to the AI velocity paradox.
AI coding assistants speed up development, but they can also hurt stability. Google’s DORA report links a 25% increase in AI adoption to a 7.2% drop in delivery stability. Your testing infrastructure and CI/CD pipelines were built for human developers, and they can’t keep up with the volume, velocity and patterns of AI-generated code.
So the question is: how do you validate AI-generated code without becoming a bottleneck?
New Speed of Development
The adoption of AI coding assistants happened fast. They didn’t just add a feature to your development workflow; they fundamentally changed the pace at which software gets written.
AI is everywhere in your pipeline, and 76% of developers rely on AI for everything from code generation, documentation and bug fixes to test creation. Most of them accept close to 30% of AI suggestions and retain 88% of the generated code in their pull requests. This isn’t a pilot project anymore; it’s the way your team works.
AI coding assistants have cut the time spent on coding and boilerplate generation from hours to minutes, and that led to a massive increase in the volume of PRs.
But while everything else gained pace, code review capacity stayed flat. In fact, the amount of code requiring review doubled. Your existing test infrastructure and processes struggled to keep pace with AI-generated code.
The bottleneck wasn’t “how fast can we code?” anymore. It was “how fast can we validate that this code is safe to ship to production?”
The Quality Problem Nobody Talks About
While AI accelerates coding tasks, it introduces failure modes that differ from those of human developers. To address the validation problem, you first need to understand the quality drawbacks of AI coding assistants.
Security Vulnerabilities at Scale
One study analyzed more than 100 large language models (LLMs) and found that 45% of AI-generated code contains OWASP Top 10 security vulnerabilities. Many of the models also generated code with design issues. There have also been reports of the tools themselves introducing risk, like leaking secrets in repositories.
Why AI Code Fails Differently
AI coding assistants generate code that is syntactically correct but, unfortunately, contextually wrong. They don’t fully understand your application’s architecture, business rules or security model. For example:
- SQL injection vulnerabilities may arise because the model learned from insecure examples during training.
- Authentication checks might be omitted if the prompt doesn’t explicitly request them.
- Validation logic can be missing because the model tends to optimize for brevity and functional output, not robustness or security.
Edge cases are where AI coding assistants fail most. Experienced developers consider failure scenarios: What if the database is down? What if the input is incorrect? What if there’s a network failure? AI predicts what statistically comes next in the code, not what can go wrong in production.
The Trust Gap
AI now writes roughly a quarter of production code, and 69% of organizations have found vulnerabilities introduced by AI-generated code. Yet the code review process hasn’t adapted to the new way of coding. Teams now get far more code to examine with the same capacity. Reviews become more superficial, and critical flaws slip through because the team is overwhelmed.
Continuous Validation: The Answer
When AI generates code, your validation needs to match its speed, and more code reviews can’t achieve that. It requires an automated, continuous validation approach.
The Architecture
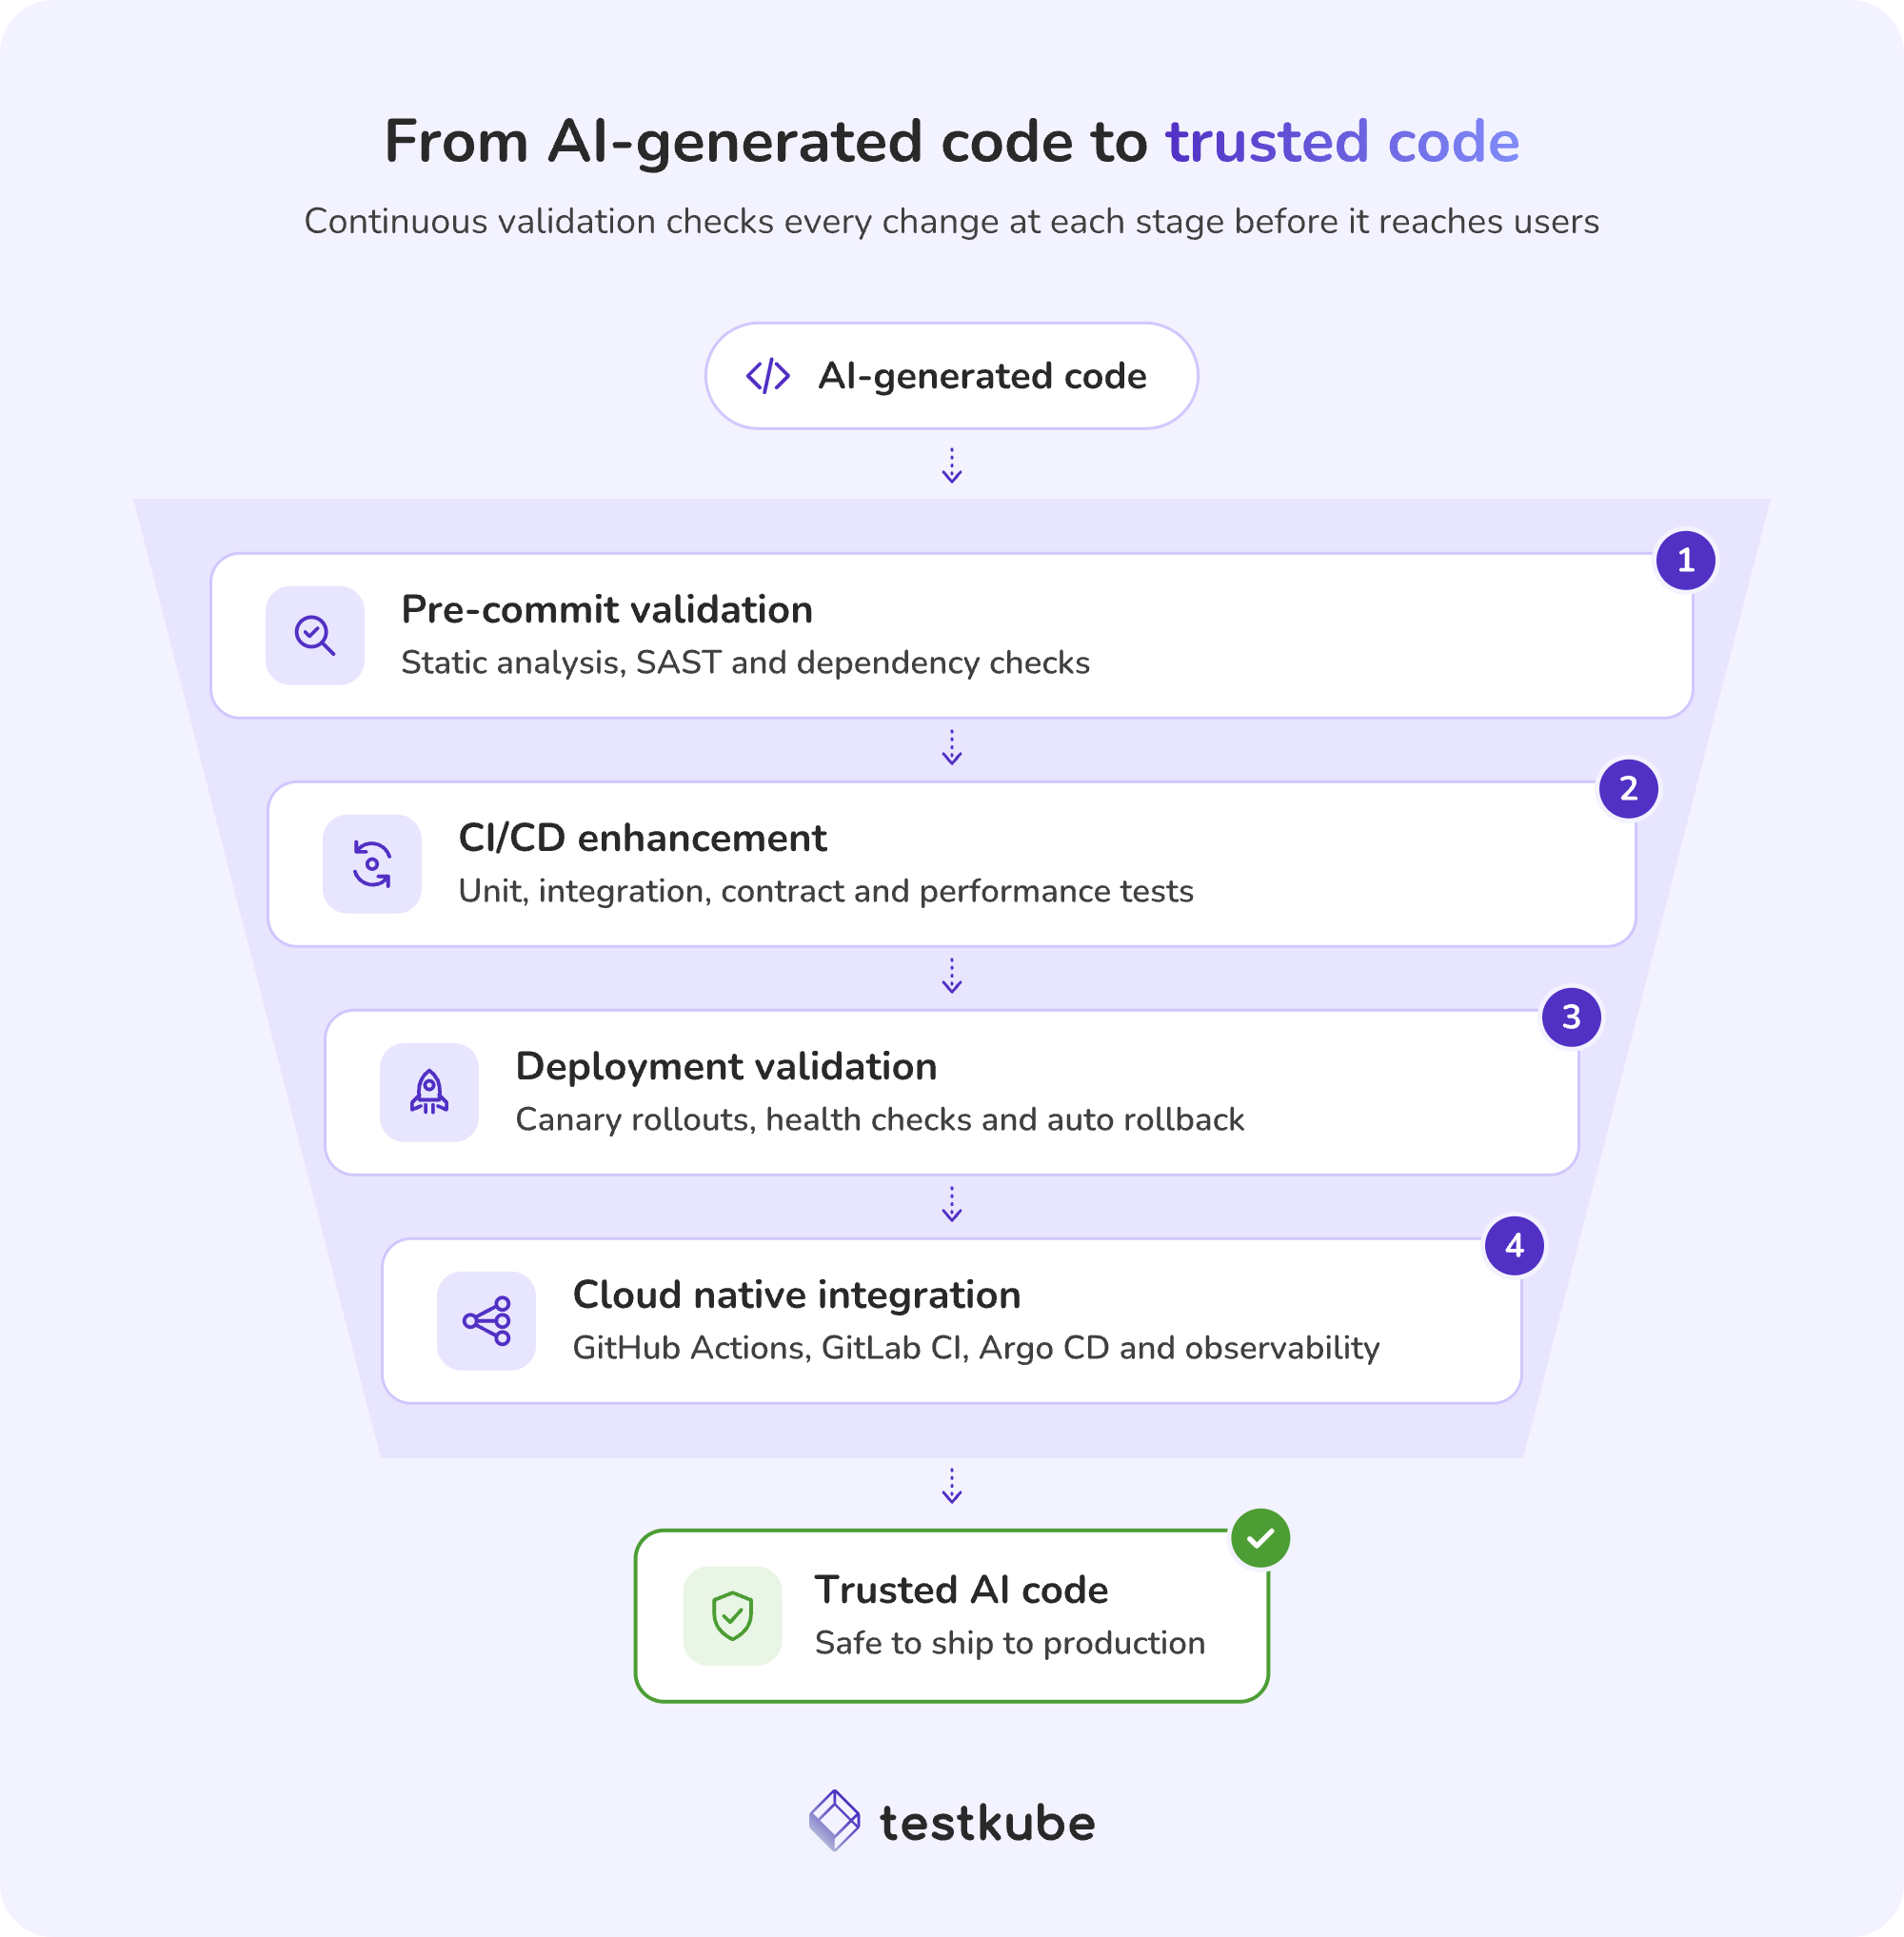
Validation must happen at every stage, from pre-commit and pre-merge through deployment and production, not only as the final gate before release. Traditional CI/CD pipelines test code in batches. Continuous validation means testing constantly, with AI-aware quality gates designed for AI-generated code.
Pre-commit Validation
This layer intercepts issues before the code even enters version control. Static analysis tools look for AI code patterns known to cause problems. Security scanning (SAST) looks specifically for AI-generated vulnerabilities like missing input validation or weak authentication. Automated dependency checks can catch hallucinated packages: non-existent libraries that AI sometimes invents.
CI/CD Enhancement
The CI/CD pipeline must scale to match the volume of AI-generated code: unit tests for functions, integration tests for services and end-to-end tests for workflows. Contract tests validate that API changes don’t break production. Performance benchmark tests can catch the resource-intensive code that AI sometimes generates. Lastly, a quality gate blocks merges if anything fails in the pre-commit stage or if coverage drops.
Deployment Validation
The deployment validation layer keeps releases safe. Instead of exposing new changes to all traffic, you can use canary deployments with automated health checks to test changes on a small set of users first. Progressive rollout practices monitor real-time metrics and can trigger automated rollbacks on failure signals, often before your customers notice. In Kubernetes environments, you can use admission controllers that enforce security policies at the cluster level.
Cloud Native Integration
All your continuous validation tools and workflows must integrate with your existing stack, such as GitHub Actions, GitLab CI and Argo CD. Service meshes like Istio or Linkerd handle runtime checks and traffic management, while observability platforms like Prometheus and Grafana provide quick feedback on code behavior in production.
Building the Trust Framework
Move from “trust by default” to “zero trust.” Every line of AI-generated code must prove itself safe before moving to the next stage of the development lifecycle. Enable fast feedback loops so developers can fix issues while the context is fresh. Track DORA metrics like MTTR, deployment frequency and change failure rate to confirm whether your changes are working.
The Culture Layer
Changes in the technical layers are good, but you need cultural changes to reap the benefits. Developers need to adopt new ways of working with AI coding assistants. They should prompt AI to generate testable, modular code and ask it to write unit tests for its own code. They can also deploy agents at critical points to measure testability and code quality, enforce coverage standards and block merge requests if any of these checks fail.
Conclusion: Speed Without Safety Is Unsustainable
Over 20 million developers use AI coding assistants, and adoption keeps growing. AI development velocity isn’t a trend anymore; it’s the baseline for competitive software development.
But as the saying goes, with great power comes great responsibility. Velocity without validation is a debt you’ll pay in production incidents and security breaches. Traditional testing infrastructure, designed for human coding and reviews, can’t keep up with the pace of AI-generated code.
Continuous validation bridges this gap. It matches AI’s code generation speed with automated, AI-aware checks at every stage.
The next step is clear: build a continuous validation framework that runs as fast as AI writes code. Implement pre-commit checks and quality gates that block vulnerable code. Use progressive delivery to validate changes with a small set of users, and build a culture that matches the speed of AI.
Testkube provides continuous testing infrastructure for cloud-native applications. Run automated tests at any stage using Test Workflows, validating code quality, security and performance before deployment. Build the validation framework that matches AI development speed. Get started with Testkube.
Frequently Asked Questions
Continuous validation is an automated approach that checks code at every stage of delivery: pre-commit, CI/CD, deployment and production. Instead of relying on more manual code reviews or a single final gate before release, it uses AI-aware quality gates that keep pace with the volume of code AI assistants produce.
AI coding assistants often produce code that is syntactically correct but contextually wrong. They don't fully understand your architecture, business rules or security model, so they can omit authentication checks, skip input validation and miss edge cases like database outages or network failures. Veracode's research found that 45% of AI-generated code contains OWASP Top 10 vulnerabilities.
Pre-commit validation should include static analysis for AI code patterns known to cause problems, SAST security scanning for issues like missing input validation or weak authentication, and dependency checks that catch hallucinated packages, the non-existent libraries AI sometimes suggests.
Canary deployments release a change to a small set of users first, with automated health checks watching real-time metrics. If those checks detect failure signals, an automated rollback can revert the change before most customers ever see it.
Track DORA metrics such as mean time to recovery (MTTR), deployment frequency and change failure rate. Together they show whether you are shipping AI-generated code faster without increasing the number of changes that break production.
Testkube provides continuous testing infrastructure for cloud-native applications. Test Workflows let you run automated functional, security and performance tests inside your Kubernetes clusters at any stage, triggered from CI/CD tools like GitHub Actions and GitLab CI or from progressive delivery tools like Argo Rollouts.
{{banner-get-started}}
About Testkube
Testkube is the open testing platform for AI-driven engineering teams. It runs tests directly in your Kubernetes clusters, works with any CI/CD system, and supports every testing tool your team uses. By removing CI/CD bottlenecks, Testkube helps teams ship faster with confidence.
Get Started with a trial to see Testkube in action.