

Table of Contents
Table of Contents
Further Reading
What software testing applications cover
Development, QA, DevOps, and security teams use these tools to validate software. Most teams combine five to eight of them across the lifecycle.
Why software testing applications matter
Modern systems are too complex for manual testing alone.
- Faster releases: repetitive tests run automatically
- Early detection: issues found before production
- Accuracy: reproducible, consistent results
- Broad coverage: web, mobile, API, and desktop platforms
- Continuous testing: validation built into CI/CD
- Compliance: auditable testing records
- Insights: reports, dashboards, and analytics
How software testing applications work
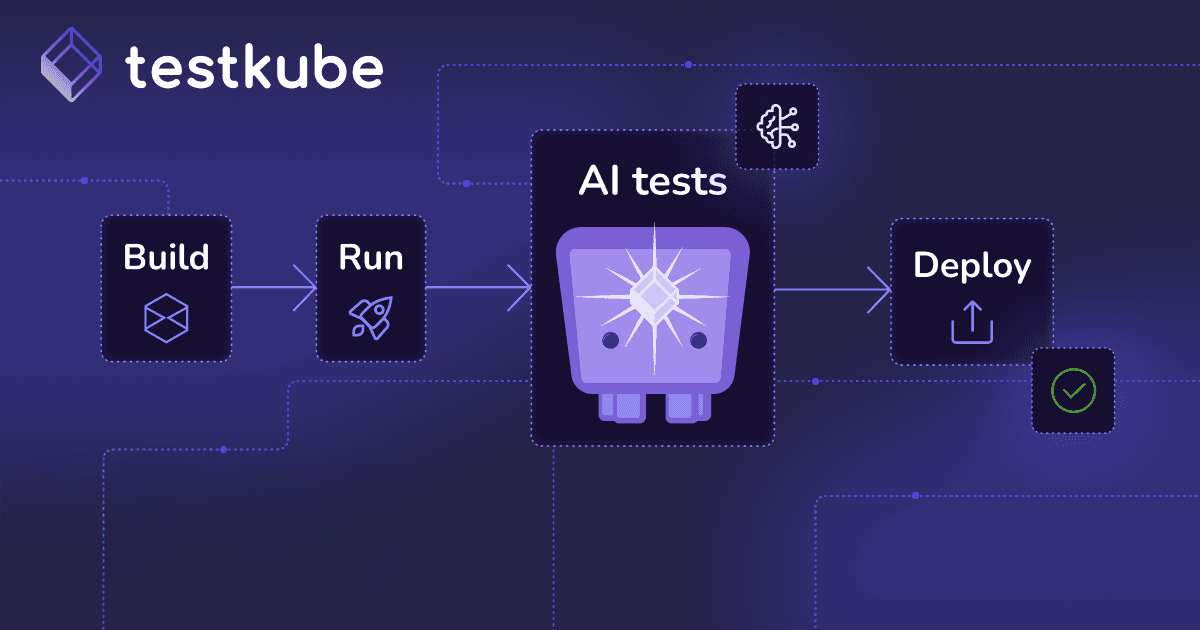
These tools validate software automatically or semi-automatically during development and delivery. Most connect to CI/CD through plugins, CLI hooks, or webhooks.
Running them inside Kubernetes through orchestration makes execution consistent everywhere.
The 7 core categories of software testing applications
1. Test management applications
These tools organize requirements, test cases, execution, and reporting.
Common examples: Jira with Zephyr or Xray, TestRail, TestLodge, qTest.
When to use: teams running manual and automated tests or reporting coverage.
2. Test automation applications
These tools run scripted tests of functional behavior on web, mobile, API, and desktop.
Common examples: Selenium, Cypress, Playwright, Appium, Postman, REST Assured, TestComplete, Ranorex.
When to use: regression, smoke, and integration tests.
3. Performance testing applications
These tools simulate user load to measure system response.
Common examples: Apache JMeter, k6, Gatling, LoadRunner, NeoLoad, Locust, Artillery.
When to use: before major releases, before peak traffic, and on a schedule.
4. Security testing applications
These tools find vulnerabilities in code, APIs, and running systems.
Common examples: OWASP ZAP, Burp Suite, Nessus, Snyk, Trivy.
When to use: every release of a public-facing application.
5. Static analysis applications
These tools inspect source code without running it to find bugs and security issues.
Common examples: SonarQube, Checkmarx, Fortify, ESLint, Pylint, SpotBugs.
When to use: from day one of any project.
6. Mobile testing applications
These tools validate behavior across devices, operating systems, and form factors.
Common examples: Appium, BrowserStack, Sauce Labs, LambdaTest, Android Studio, Xcode.
When to use: any application with a mobile presence.
7. AI-powered testing applications
These tools use machine learning to generate tests and self-heal selectors.
Common examples: mabl, ACCELQ, Functionize, Testim, testRigor.
When to use: when test maintenance grows faster than development.
Software testing application categories at a glance
Each category fits a different stage of the delivery lifecycle.
Software testing applications by platform
Different application types need different testing approaches.
How software testing applications relate to Testkube
Testing applications each focus on one area and often run in isolation. Testkube is a test orchestration platform that runs them inside Kubernetes and centralizes the results.
- Unified orchestration: many frameworks run with the same triggers and reporting
- Scalable execution: tests spread across pods and clusters
- Environment parity: tests run where applications run
- Central observability: logs, metrics, and artifacts in one dashboard
- AI-ready automation: AI agents can trigger and analyze tests through the Testkube MCP Server
Consider a SaaS team with separate tools for UI, API, load, and security tests. Testkube gives them one place to run everything and one answer to whether a release is ready.
Best practices for choosing software testing applications
Match tools to your stack and release cadence
A quarterly Java release needs different tools than daily microservice deploys.
Containerize testing applications
Tools that ship as containers run cleanly in Kubernetes and behave the same everywhere.
Integrate with CI/CD and observability
Report test results into the same Prometheus and Grafana stack as production.
Automate execution and reporting
Manual triggers and spreadsheet reports do not scale past a small team.
Use orchestration for multi-framework scale
Once the stack passes two or three tools, an orchestration layer keeps it manageable.
Common pitfalls
- Isolated tools: each application managed separately
- CI/CD-only execution: long suites block pipelines
- No aggregation: results never combined
- No environment parity: tests run far from real conditions
- Unused automation: tools bought but not fully automated