Table of Contents
Start your free trial.
Start your free trial.
Start your free trial.


Table of Contents
Executive Summary
Every enterprise in a regulated industry carries the same baseline obligation: the code running in production must be governed. Compliance frameworks demand it, security teams require it, and auditors ask for proof of it. It includes policy enforcement, auditability, and consistent quality control. SOC 2 compliance, security baselines, and risk management are the foundations that keep production systems reliable and trustworthy.
The problem is that the tooling most organizations rely on to enforce governance (manual reviews, approval chains, pre-release checklists) was built for a pace that AI-assisted development has already left behind. AI-generated code is now a regular input into your systems, written by agents and increasingly autonomous pipelines.
Engineering teams need to rebuild governance as a continuous, automated function of the pipeline that scales with AI velocity. This blog highlights that the key is shifting governance from a reactive checkpoint at the end of the pipeline to a continuous function embedded directly within it.
Why AI-generated code impacts governance
In today's world, large language models are capable of designing system architectures, creating entire applications, implementing APIs, generating tests, and writing infrastructure as code. The developer's role is shifting from writing code to reviewing what an AI system has generated.
- Along with the volume of code, what has changed is that the reviewer no longer knows whether a particular implementation choice came from a developer or from AI. The beauty of AI-generated code is that it rarely fails unit tests, making it much more difficult to identify gaps.
- Traditional governance was architected around a human at every decision point. A human wrote the code, a human reviewed it, a human signed off on it. Every approval chain, audit trail, and compliance checklist assumed that bottleneck existed and used it as the control mechanism.
- AI does not remove that bottleneck. It shifts and magnifies it. The code keeps arriving, faster, in higher volume, with fewer visible seams, but the governance infrastructure stays the same size.
- Frameworks like SOC 2, ISO 27001, and DORA require concrete proof of executed controls (e.g., security checks, RBAC validation, policy verification). These controls need to scale to match the volume of AI-generated code.
- Uncaught policy violations reaching production can compromise audit standing, trigger regulatory penalties, and require costly post-incident remediation. AI is making governance harder.
What continuous governance means in practice
Governance needs to be treated the way modern platform engineering teams treat infrastructure policy. This means you define the rule, enforce it everywhere the artifact moves, and generate the audit trail automatically. It also requires reviewing and updating the rule as part of enforcement, with real validation, rather than as a separate documentation exercise.
The same logic applies to AI-generated code across the SDLC with Governance as Code. Governance as Code means writing security, compliance, and governance rules as code so they can be versioned, tested, and automated. You distribute smaller, automated checks for governance rules across every stage where AI output enters the pipeline. The rule runs, the result is logged, and the evidence exists at the moment enforcement happens.
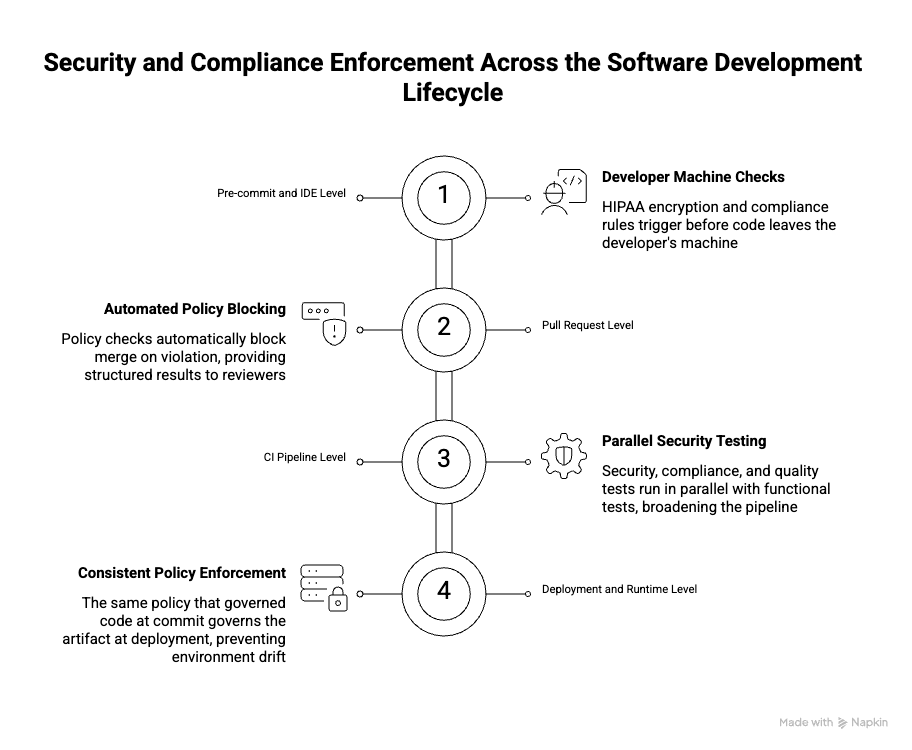
How Testkube enables governance as code
Testkube runs security and compliance tests independently from code delivery pipelines. It can act as the execution layer that operationalizes governance controls. The audit requirements are met through scheduled testing that does not block developer workflows. Tests trigger from CI/CD systems, manually, on a schedule, via APIs, or by Kubernetes resource changes. A compliance check fires the moment AI-generated code enters the pipeline, not when someone remembers to run it.
Here is what this looks like against a real compliance rule. HIPAA and SOC 2 both require TLS 1.2 or higher on any API handling sensitive data. An AI coding agent generating a patient data endpoint will produce code that passes unit tests and deploys cleanly and may still accept plain HTTP connections.
Build-time governance
Build-time checks catch policy violations at the point the code is written and merged. This is the earliest enforcement layer, before the artifact is built, before it reaches staging, before any infrastructure is involved.
An AI coding agent generating a patient data endpoint will produce code that passes unit tests and deploys cleanly and may still accept plain HTTP connections. Catching that at pull request costs a one-line fix. Catching it in production costs a breach notification.
A k6 TestWorkflow in Testkube enforcing this rule:
- Triggers automatically on every pull request touching a data service
- Checks that the endpoint rejects plain HTTP and enforces TLS 1.2 or higher
- Blocks merge on failure with a structured result naming exactly which endpoint failed and which rule it violated
- Writes a timestamped, versioned result to the audit log as a byproduct of running, with no separate documentation step
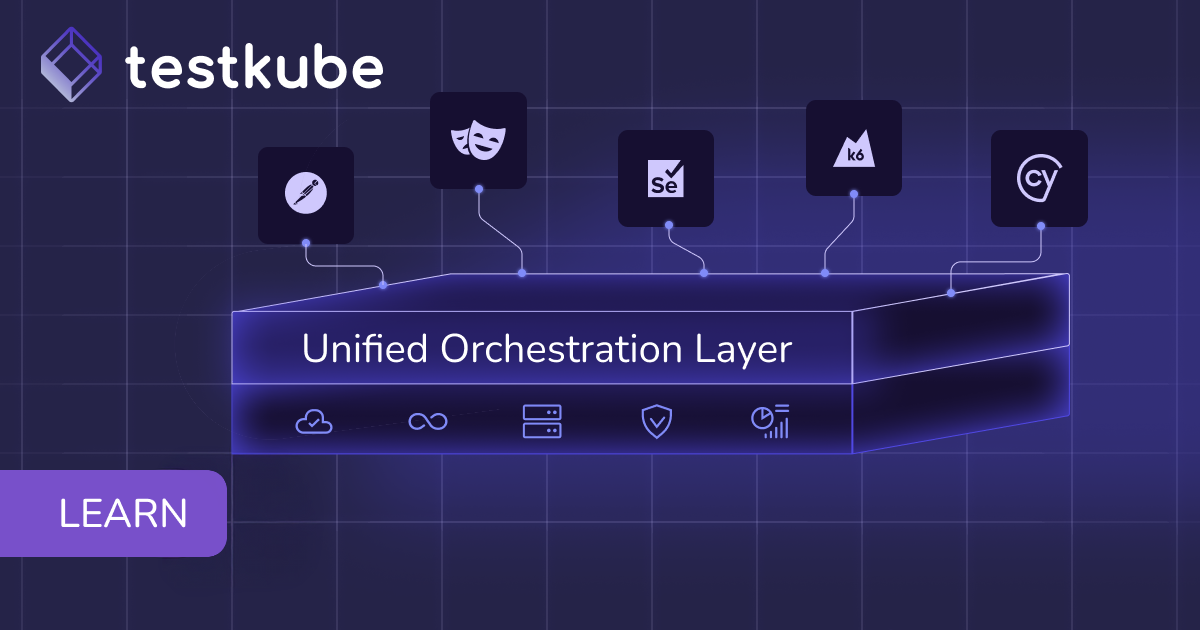
Testkube orchestrates the testing frameworks teams already use (Cypress, Playwright, k6, JMeter, Postman, or Selenium), so governance runs on existing test investment rather than requiring a parallel toolchain. Testkube with k6 enables teams to validate API-level security posture at scale: enforcing TLS versions, verifying encryption in transit, validating authentication headers, and confirming proper HTTP redirect behavior, all as runnable, repeatable compliance checks.
Deploy-time governance
Build-time checks catch what the code does. Deploy-time checks catch what the infrastructure allows. A TLS enforcement rule that passed at pull request can still be violated by a configuration change to an Ingress, a ConfigMap update that modifies environment variables, or a deployment that introduces a new image with different security settings. None of these trigger a CI pipeline. Without deploy-time governance, they reach production unvalidated.
Testkube TestTriggers solve this by binding compliance test execution directly to Kubernetes events rather than to pipeline events. A TestTrigger listens for changes to specific Kubernetes resources (a Deployment update, an image change, a ConfigMap modification) and fires a TestWorkflow the moment that event occurs. No pipeline run required, no human remembering to recheck.
A TestTrigger enforcing the same TLS rule at deploy time:
- Watches for any Deployment update, image change, or ConfigMap modification in namespaces handling patient data
- Fires the TLS validation workflow automatically when the cluster state changes
- Checks that the live endpoint still rejects plain HTTP and enforces TLS 1.2 or higher against the running service, not the source code
- Blocks or flags the change if the live configuration violates the rule, with the same structured, timestamped audit result written to the control plane
This is useful in GitOps scenarios where deployments are reconciled by tools like ArgoCD or Flux rather than triggered by a pipeline. TestTriggers fire when the cluster state is updated, meaning governance runs in response to what actually changed in the cluster, not what the pipeline thinks changed. Listener Agents can watch for changes in one cluster and trigger test execution in another, which means a configuration drift in a production cluster can trigger validation tests running from outside that cluster, preserving network-level accuracy.
Governance that scales with AI
Once Governance as Code is running through Testkube, three things follow that manual governance cannot produce simultaneously: consistent enforcement at scale, developer autonomy inside guardrails, and compliance evidence that builds itself.
Scale (H3)
Testkube connects each cluster through lightweight Runner Agents that link back to a unified control plane. Teams define governance policies and test definitions once, then deploy them uniformly across every connected environment. No need to maintain separate compliance test suites per cluster.
For organizations operating across multiple cloud providers and geographically distributed clusters, this means governance policy enforcement scales without proportional operational overhead. TLS validation, encryption checks, and authentication rules run identically everywhere without requiring parallel test infrastructure per platform.
A compliance rule defined once in the control plane propagates automatically to every agent in every cluster. A new HIPAA encryption check runs in development, staging, and production without any team needing to configure it separately.
Speed
Platform engineers enable self-service testing through centralized control and governance while developers trigger specific test suites without needing to understand Kubernetes YAML or complex CI/CD configuration.
When observability is built in and guardrails are clear, teams move faster without sacrificing reliability or compliance. Developers get immediate, specific failure feedback naming exactly which rule failed, not a security backlog item to resolve days later.
Evidence
Testkube keeps workflow definitions in Git and maintains an audit trail that enables rollback. Every execution is timestamped, traceable, and versioned. SOC 2 Type II audits evaluate controls over a period of time, meaning teams must produce continuous logs and activity records, not a point-in-time snapshot assembled before the auditor arrives. Testkube produces exactly that record as a byproduct of enforcement.
Continuous automated evidence collection is far more reliable than reconstructing months of history by hand. Evidence produced by enforcement reflects what actually ran, not what someone intended to run. For EU AI Act compliance, the technical documentation and record-keeping obligations under Articles 8-15 require evidence of what ran, when, and against what policy. Automated test execution creates that record continuously rather than requiring manual assembly before an assessment.
Conclusion
AI-generated code is not inherently dangerous, but its quality varies depending on the LLM used to create it. The answer is not fewer controls. It is controls that run at the same speed as the code, produce evidence automatically, and stay out of the developer's path. Governance as Code, where compliance rules are versioned, tested, and enforced automatically at every stage the artifact moves through, is the only model that scales with AI velocity without turning governance into a bottleneck.
Testkube gives enterprises exactly that: governance, auditability, and policy enforcement at pipeline speed. Build-time checks catch violations before code is merged. Deploy-time TestTriggers catch configuration drift before it reaches production. Audit trails are produced as a byproduct of enforcement running continuously, not assembled the week before an audit. And because Testkube orchestrates the testing frameworks your teams already use, governance runs on existing investment rather than requiring a parallel toolchain.
Engineering teams keep moving. Compliance evidence keeps building. The gap between AI velocity and governance capacity closes, not by slowing the code down, but by making the controls fast enough to keep up.
Frequently asked questions
About Testkube
Testkube is the open testing platform for AI-driven engineering teams. It runs tests directly in your Kubernetes clusters, works with any CI/CD system, and supports every testing tool your team uses. By removing CI/CD bottlenecks, Testkube helps teams ship faster with confidence.
Get Started with a trial to see Testkube in action.